AI & ML
Malware Detection and Classification
This project examines malware detection and classification directly from raw executable byte sequences, avoiding heavy manual feature engineering.
Back to Research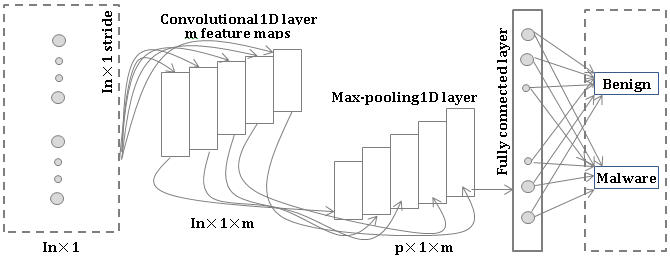
Project Summary
Executable byte-sequence analysis to detect malicious patterns and improve cybersecurity response.
Traditional malware analysis often depends on handcrafted features or costly preprocessing, which can miss important byte-level structure in executable files. Identify malicious patterns directly from raw byte streams and improve malware-family classification robustness. The project analyzes raw byte sequences of executable files such as Windows PE binaries to detect suspicious behavior. The MalFormer direction treats malware analysis as a sequence modeling problem over binary content. The overall aim is to strengthen detection quality while reducing dependence on manual feature design.